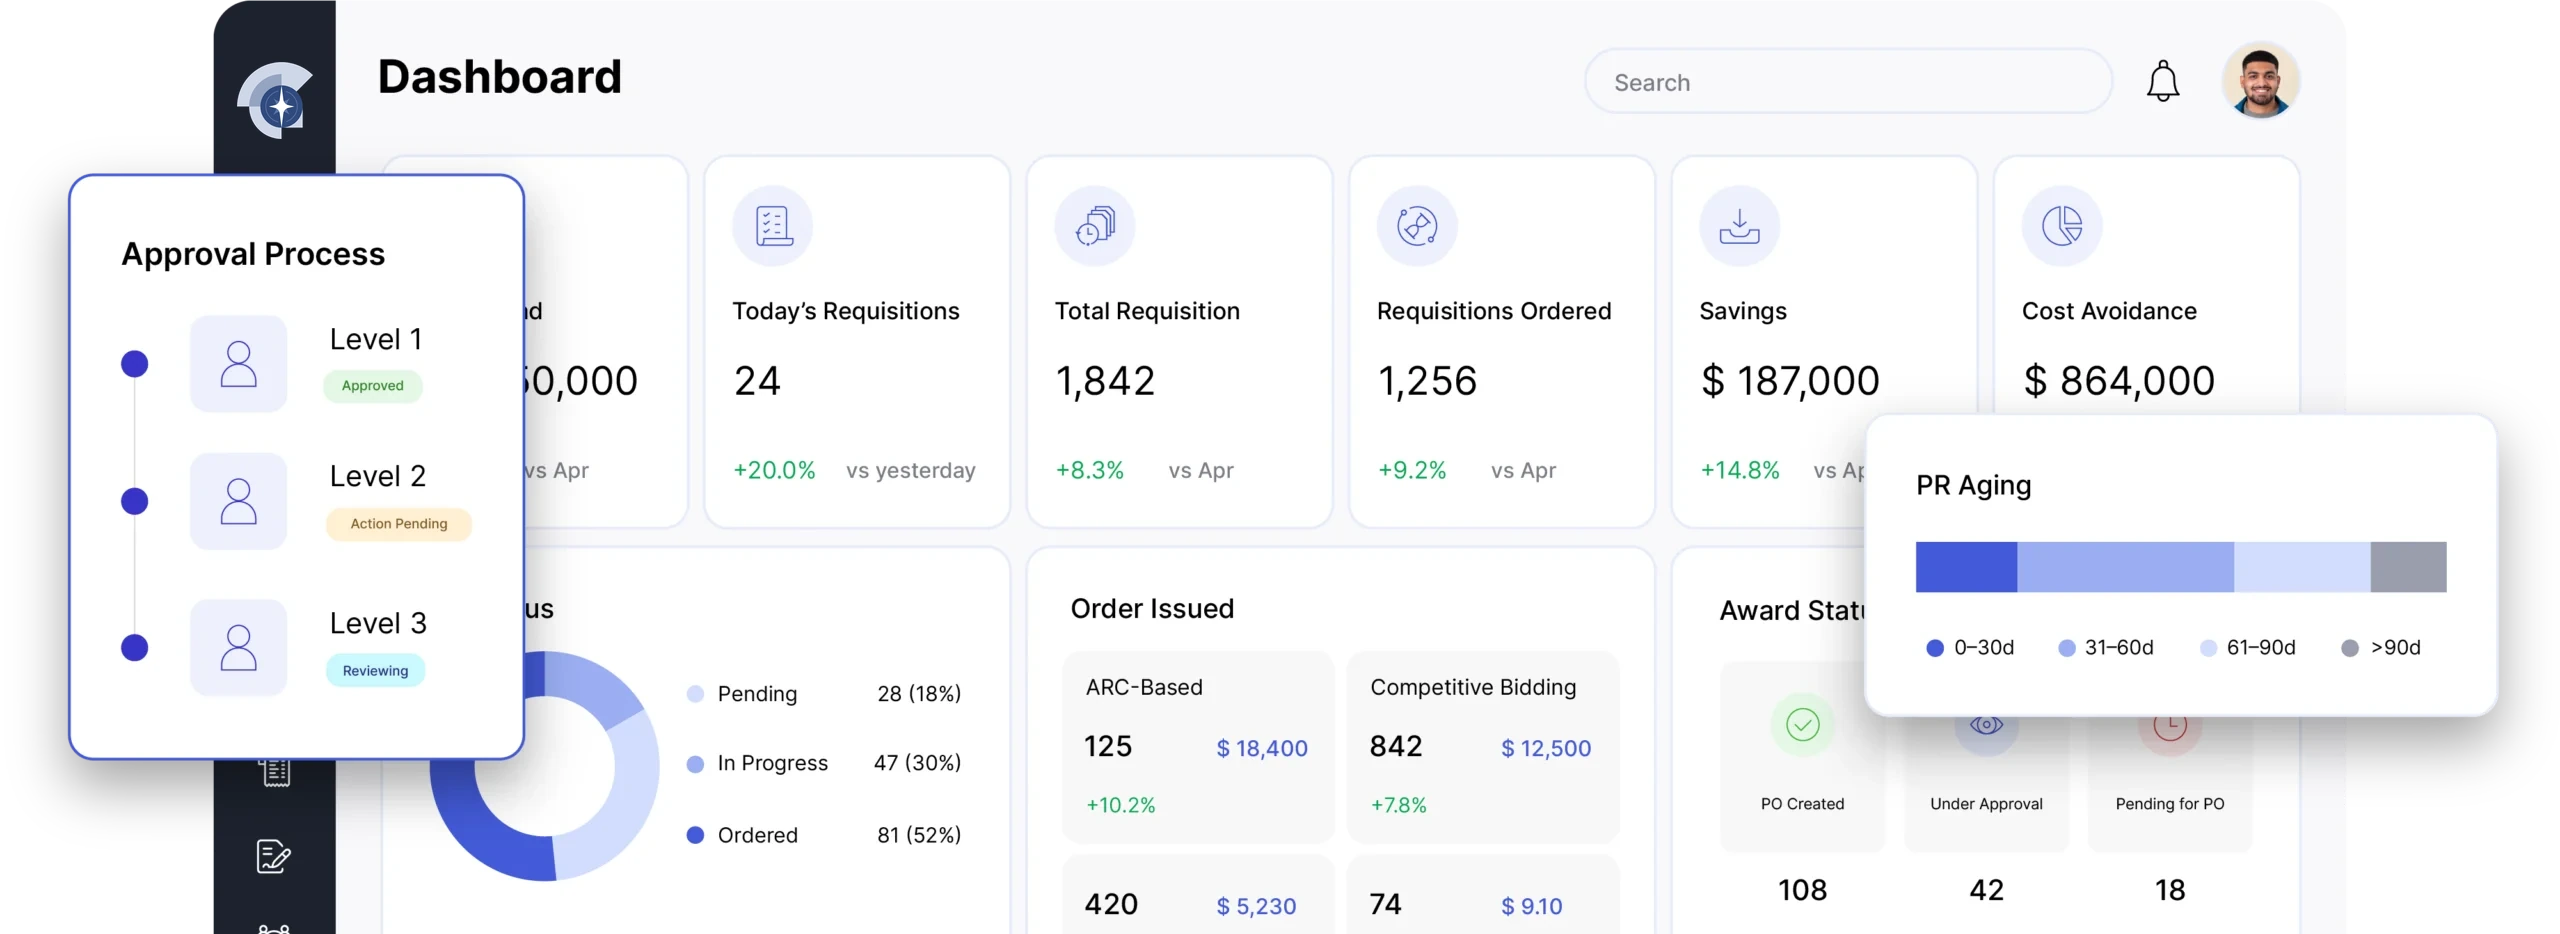
Business and procurement owner
Defines the commercial need, supplier relationship, outcome, and obligations that matter in practice.
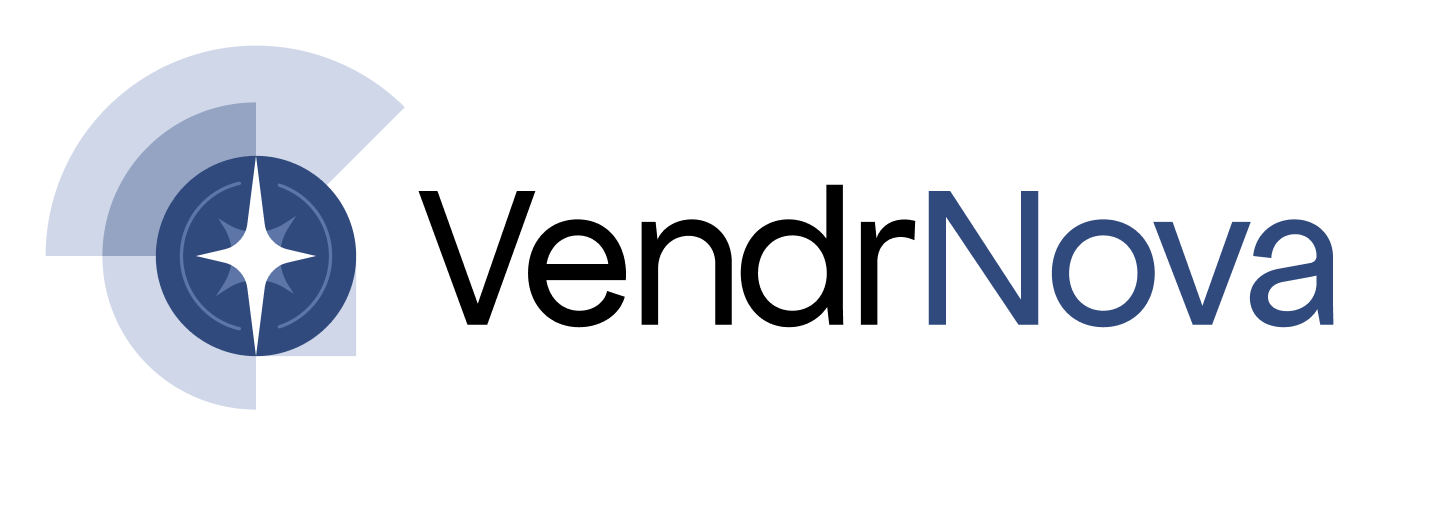
Contracts & Compliance
Turn policies into visible, practical guardrails that help teams move quickly while keeping decisions accountable.
Who this is for
Policy and Compliance Management is for enterprises where policies exist, but employees, approvers, buyers, and suppliers experience them as documents, exceptions, or late-stage checks.
Buyer lens
The buying question is not only whether this capability works. It is whether the right people can use it, govern it, and carry the context into the next step.
Why teams use it
A focused capability should remove uncertainty from the people doing the work while keeping the business rules and accountability intact.
 VendrNova
Contract control
Updated just now · All entities
Active contracts
438
In view
Renewals ahead
31
90 days
Linked spend
$18.4M
Connected
Exceptions
12
Assigned
Active contracts
438
Linked spend
$18.4M
Exceptions
12
Workflow before and after VendrNova
The value of a module is clearest when buyers can see how the work changes before, during, and after the handoff.
Before VendrNova
The organization depends on knowledge, memory, and retrospective review to keep everyday purchasing compliant.
Requesters and buyers decide what applies because the policy is not connected to the specific purchase context.
Approvers see exceptions late and do not always have a consistent reason, owner, or remediation path.
Audit and leadership teams reconstruct how a decision followed or departed from policy.
With VendrNova
The workflow makes the expected route easier to follow and the exception easier to understand, approve, and improve.
Use category, entity, threshold, supplier, contract, budget, and risk context at the relevant step.
Show why the path changed, who can approve it, what evidence is needed, and what happens next.
Use decisions, exceptions, and outcomes to improve policy and adoption over time.
Roles involved
Enterprise adoption improves when each stakeholder can see the part of the workflow they own and the context they need from the role before them.
Defines the commercial need, supplier relationship, outcome, and obligations that matter in practice.
Reviews terms, risk, policy, exceptions, and the evidence required for an accountable agreement.
Connects commercial commitments to budget, authority, payment, and downstream control.
Makes obligations, renewals, supplier commitments, and workflow status usable after signature.
Integration, ERP, governance, and security
A commercial page should help the buying group understand what connects, what remains authoritative, and which controls need to be reviewed before rollout.
Policy decisions need reliable attributes from ERP, finance, supplier, contract, identity, category, entity, and budget systems. Define which system provides each attribute and how policy outcomes are recorded in the transaction history.
Compliance design should cover access, approval authority, separation of duties, exception reasons, evidence, retention, and the review of policy changes. Security and privacy controls should match the data and decision risk involved.
Implementation approach
Choose one policy or exception pattern that creates repeated friction. Translate it into a guided workflow, test real scenarios with users and approvers, and use the evidence to refine the rule and route.
Implementation principle
Connect the agreement to the moment it matters.
Scope the workflow around the decision, data, owners, and handoffs that need to work after launch—not only the screens that need to be configured.
Identify request, review, approval, signature, obligation, renewal, and exit points.
Define who owns legal review, business action, compliance evidence, and renewal decisions.
Link contract context to suppliers, buying paths, budgets, invoices, and exception handling.
Use templates, reminders, and review signals to scale the agreed operating model.
Customer evidence
Use the customer voice below as a starting point, then test the same workflow against your own systems, roles, controls, and priorities.
“VendrNova helped us consolidate supplier management, improve compliance visibility, and keep onboarding, approvals, and the audit trail in one place.”
G. Saraswat
DGM (MM) Procurement · FSNL Pvt. Ltd
Relevant FAQs
Clear answers help procurement, finance, IT, security, and business stakeholders enter the same conversation.
It puts procurement policies into the workflows, routes, approvals, preferred sources, thresholds, exceptions, and evidence that shape everyday buying decisions.
Yes. Policy decisions often depend on entity, category, account, cost center, budget, supplier, and threshold data. The implementation should define authoritative sources and how outcomes are recorded.
Make the exception reason, owner, approval authority, evidence, timing, and next action visible. Use the pattern of exceptions to improve policy or user guidance.
Make the expected route easier to understand and use, ask only for context needed at that moment, and provide a clear path for legitimate exceptions.
Next step for Policy & Compliance Management
Bring one policy or recurring exception to VendrNova and define how guidance, approval, evidence, and improvement should work in practice.